4 hours ago
3-year-old Radix bug triggers $1.3 million drain and 10-day halt
3-year-old bug triggers $1.3 million drain and forces 10-day blockchain halt
CryptoSlate
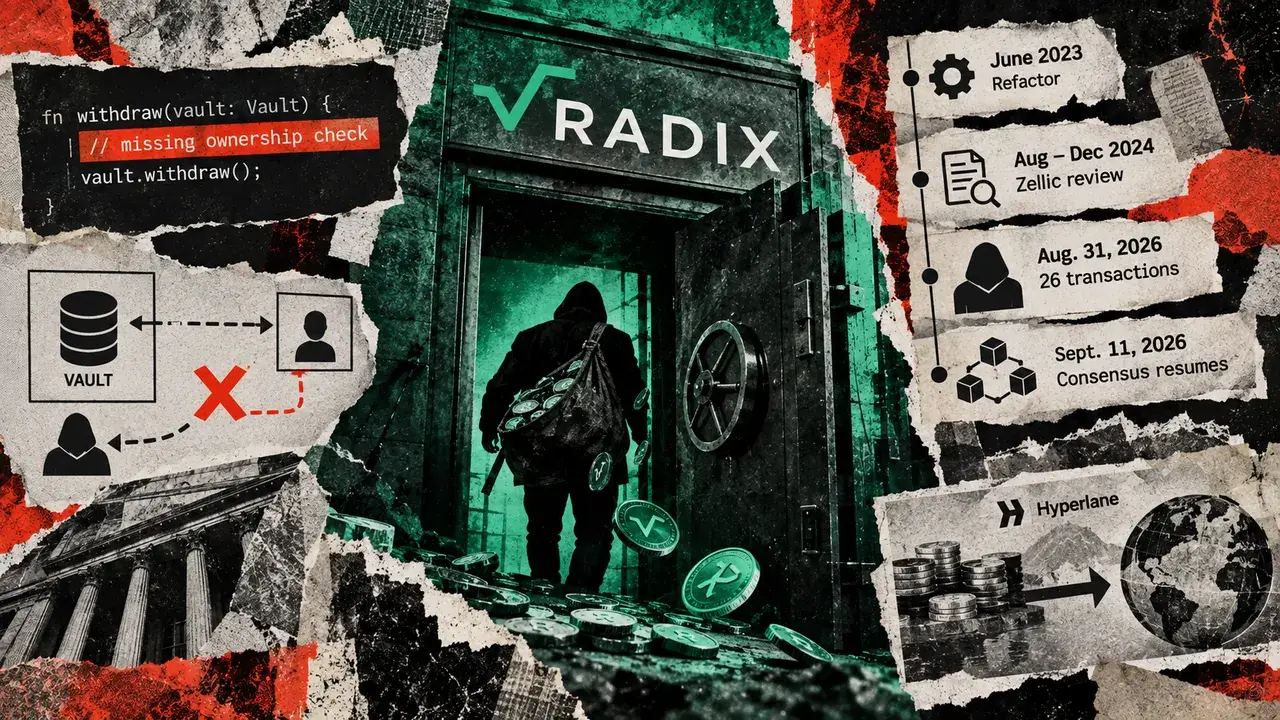
A Radix Engine flaw enabled a roughly $1.3 million theft and forced validators to halt the blockchain. The Radix Foundation said an RDX Works development team introduced the defect during a June 2023 cleanup of the Radix Engine. The vulnerability remained undetected for more than three years. An attacker exploited it on Aug. 31. A community ledger reconstruction recorded 26 exploit transactions. The attacker withdrew about 458,915 USDC. The attacker withdrew 72,420 USDT. The attacker withdrew 61.08 ETH. The attacker withdrew 6.35 wrapped Bitcoin. The attacker withdrew 536.16 SOL. The attacker withdrew 32.91 BNB. The assets were worth roughly $1.26 million using Aug. 31 market prices. The attacker took another 13,000 XRD to pay transaction fees. The two stablecoins accounted for about $531,335. The attacker sent the assets through Hyperlane to Ethereum, BNB Chain, and Solana. Radix said the attacker then sold the assets for ETH. Hyperlane operated as designed. No private keys were compromised. Investigators concluded that the flaw could have been used against any vault on the network. The potential exposure included tokens and other assets beyond the bridged holdings targeted by the attacker. Validators took enough stake offline to prevent the network from reaching consensus. This action stopped additional transactions while developers worked on a fix. The halt lasted more than 10 days. A protocol fix blocked restricted vault references from being used for ordinary withdrawals. User transactions resumed on Sept. 11, according to the community ledger reconstruction. Zellic had audited the Radix protocol in 2024. The review included the engine kernel containing the defect. The review did not detect the authorization flaw. The bug allowed a transaction to identify another user's vault through its internal address. Smart-contract code could then receive that reference. The engine allowed ordinary withdrawal functions without properly enforcing the ownership boundary. The attacker accessed assets held by user accounts, applications, and liquidity pools without obtaining the owners' signatures. The incident caused secondary losses in liquidity pools after bridged assets were removed from one side of trading pairs. Distorted prices allowed another account to extract millions of XRD from affected pools. Radix said it is adding regression tests. Radix is strengthening its security review process. Radix is formalizing the emergency procedure validators used to break network liveness. The Foundation said future security work must account for increasingly capable AI-assisted code-analysis tools. The Foundation believes those tools may have helped the attacker identify the years-old defect.
This content is an AI-generated summary/analysis for informational purposes only and does not constitute investment advice.