August 21, 12:10
Coldcard Ships Firmware After $114M Bitcoin Theft, Cites AI Review
Coldcard ships firmware after $114 million bitcoin theft; says AI helped catch more bugs
CoinDesk
Key Point
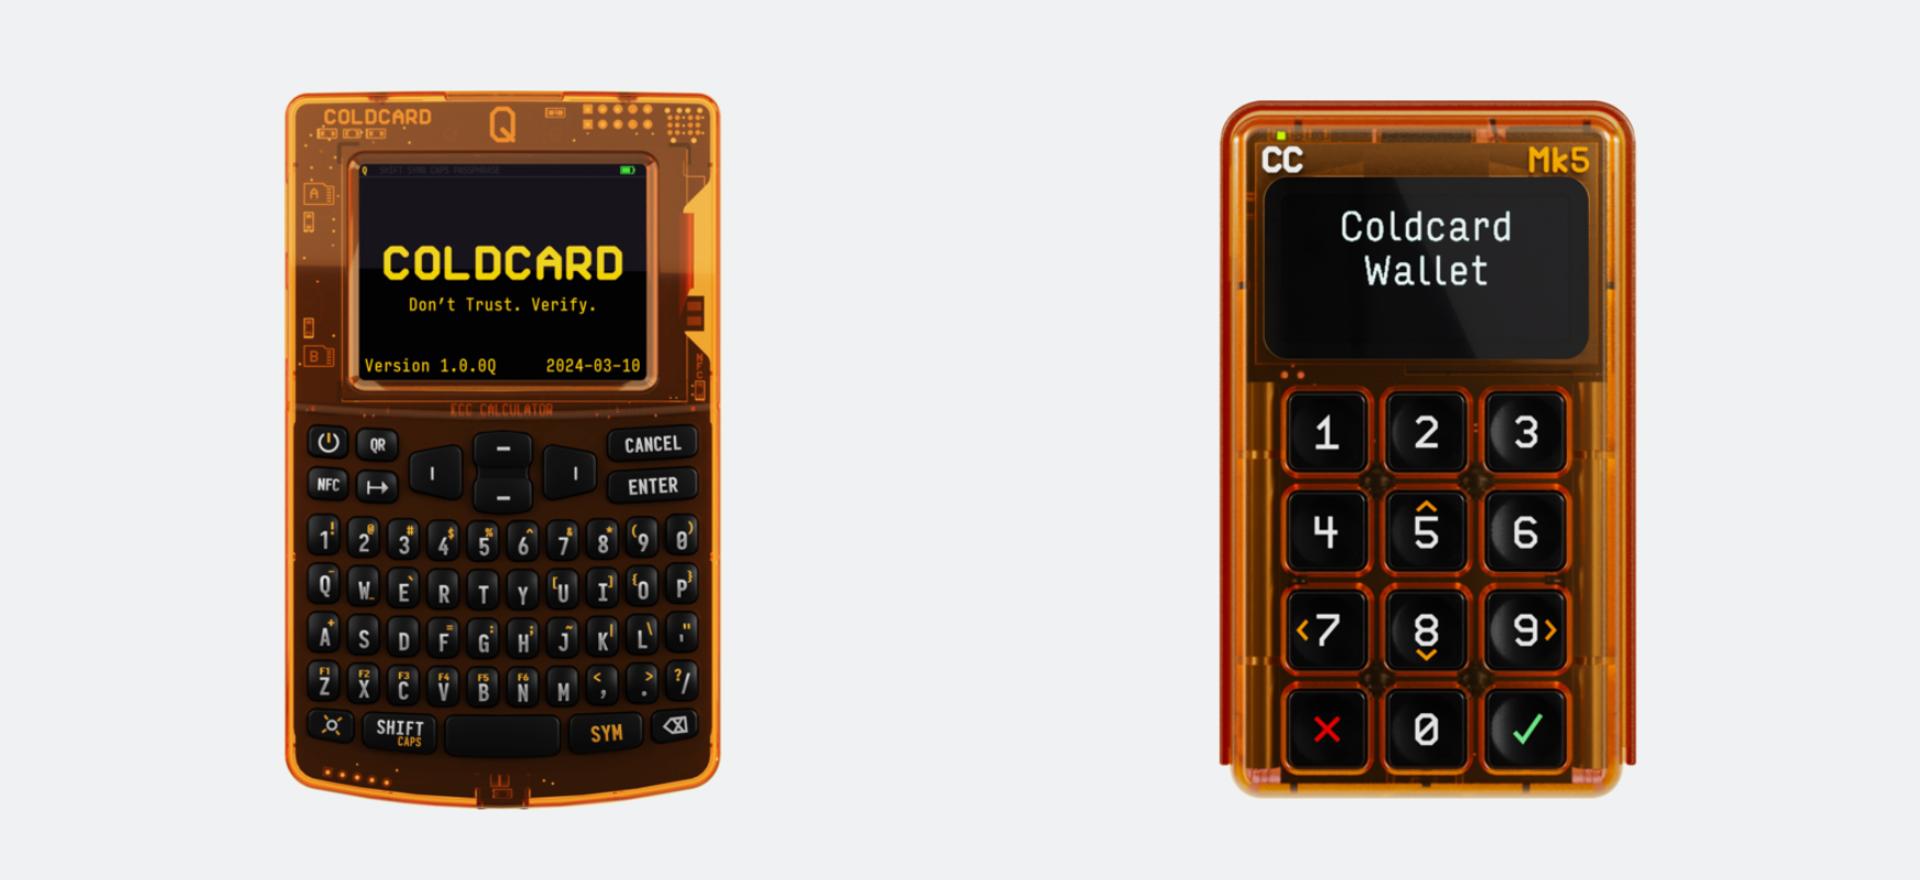
Coinkite released firmware for Coldcard hardware wallets after a randomness flaw enabled attackers to steal more than $114 million in Bitcoin. Coinkite said an AI-assisted system review found additional issues in transaction approval, USB data handling, and firmware validation. Seeds created on affected firmware between 2021 and July 2026 require replacement and fund migration even after installation. New Coldcard seeds require physical randomness through 65 unpredictable key presses, 50 six-sided die rolls, or 128 coin flips.
Market Sentiment
Cautiously Bullish, Tech-driven.
Reason: Coinkite released firmware after an AI-assisted review identified additional security issues.
Similar Past Cases
Hardware wallet security failures typically increase demand for seed replacement and cautious fund migration rather than create a lasting market-wide price effect. The current case differs because Coinkite applied an AI-assisted review across the wider Coldcard system.
Ripple Effect
The required seed migration could shift attention to wallet setup practices and transaction verification among affected Bitcoin holders. If holders complete migration promptly, the security impact may remain contained within affected Coldcard wallets.
Opportunities & Risks
Opportunities: Users can monitor whether Coldcard provides further validation details for the updated firmware and seed-generation process.
Risks: The main risk is that seeds created on affected firmware remain exposed until holders generate new seeds and migrate funds.
This content is an AI-generated summary/analysis for informational purposes only and does not constitute investment advice.