August 23, 05:00
Coldcard requires 65 key presses after seed-generation exploit
Coldcard now requires 65 key presses after seed exploit, while exposed funds still must move

CryptoSlate
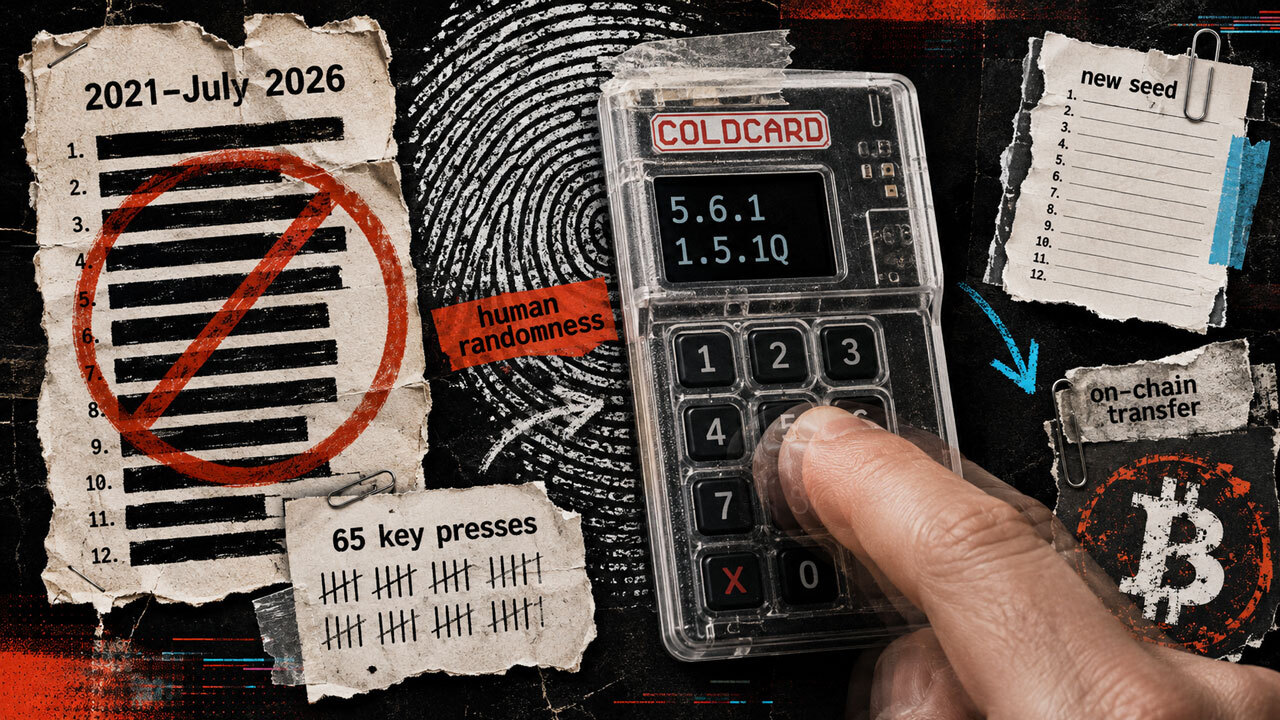
Coinkite released firmware on Aug. 20 that adds mandatory human input to new standard seeds. The process requires at least 65 key presses at unpredictable intervals. Users can instead provide 50 physical six-sided die rolls or 128 physical coin flips. The new firmware does not change seeds created by affected releases. Coinkite's migration guidance tells affected users to generate a new seed. Users must verify the backup and wallet fingerprint. Users must confirm a receiving address on the device. Users must send a small test transaction before moving all balances tied to the old seed. Migration is not required when users added at least 50 fair, independent and private die rolls through the affected workflow. Users must also have kept the roll sequence unrecorded and private. Coinkite recommends version 5.6.1 for Mk4 and Mk5 devices. Coinkite recommends version 1.5.1Q for Q devices. The official exposure list covers Mk2 and Mk3 firmware versions 4.0.1 through 4.1.9. It also covers Mk4 and Mk5 standard firmware before 5.6.0. Block's technical analysis includes Mk2 and Mk3 version 4.0.0 in the affected range. Block traced the flaw to a deterministic MicroPython fallback that could activate because a zero-valued feature flag was treated as present. Coinkite said some customers suffered severe losses. Law enforcement is investigating. Coinkite has not published a verified victim count or loss total.
This content is an AI-generated summary/analysis for informational purposes only and does not constitute investment advice.