September 28, 14:30
Bitget says it detected transfers roughly 30 minutes before $290 million moved
Bitget had 30 minutes to contain its hack before $290 million started moving

CryptoSlate
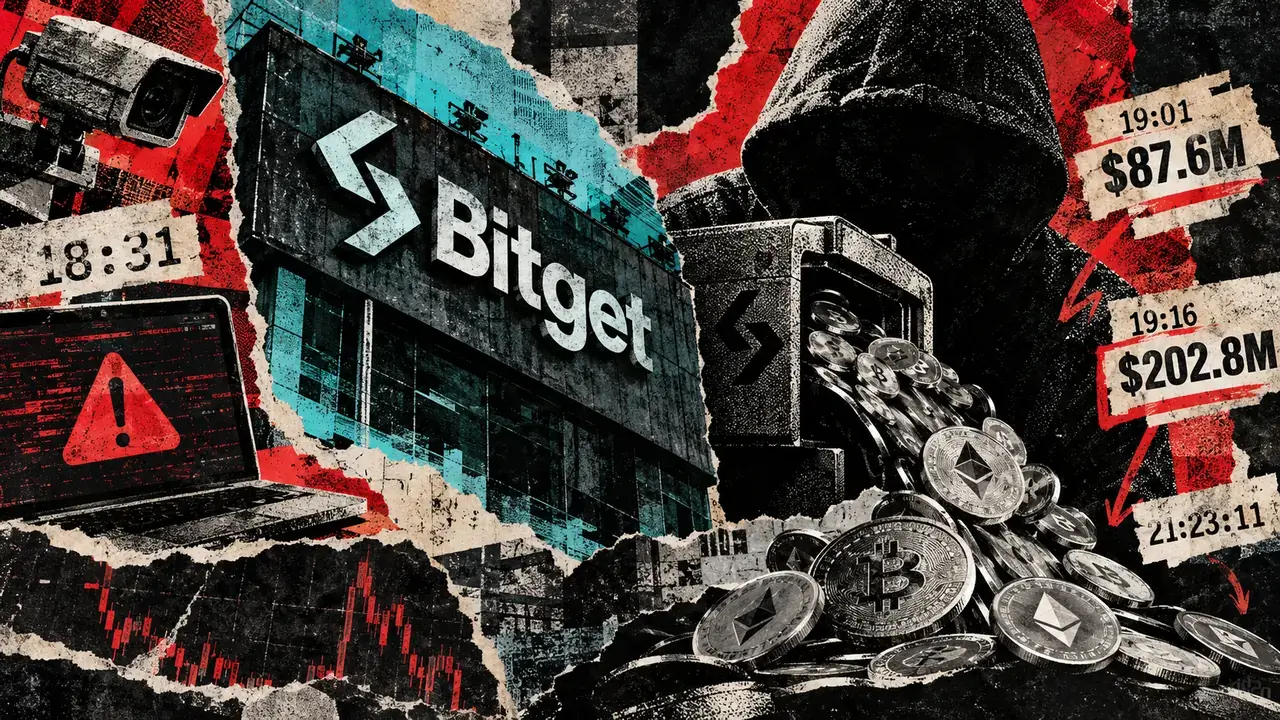
Bitget said its systems flagged unauthorized wallet transfers at 18:31 UTC on Sept. 24, about 30 minutes before attackers began the major outflows. Bitget said its security team immediately activated emergency protocols. Hypernative's reconstruction showed $87.6 million left hot wallets at 19:01. It showed another $202.8 million left warm wallets at 19:16. The two bursts took a combined 24 seconds. They accounted for about three-quarters of the $387.5 million Bitget ultimately said was moved to attacker-controlled addresses. The sequence suggested Bitget had roughly half an hour after the alert to prevent the first major wave. It suggested Bitget had about 45 minutes before the largest transfer burst. Hypernative said the attacker tested the compromised route at 18:31 with transfers of 0.84 ETH and 93 TRX to new addresses. Hypernative said the attacker waited about 28 minutes before moving $34.75 million of USDT at 18:58. The attacker then accelerated the drain across multiple blockchains. Bitget said its investigation found that the attacker compromised a backend system in its wallet infrastructure. Bitget said the attacker spoofed withdrawal data. Bitget said the attacker tricked the exchange's authorization process into approving the transfers. Bitget said private keys were not compromised. Hypernative said Bitget's own wallets signed the transactions. Hypernative said the transactions resembled ordinary customer withdrawals closely enough to pass through Bitget's infrastructure. Hypernative said a check could have required each signed transfer to match an independently stored customer withdrawal or approved treasury transaction. Hypernative said that check could have prevented a compromised backend service from creating its own authorization. Hypernative found unusual transaction parameters in the attacker's requests. Hypernative said the requests included gas limits that differed from Bitget's normal withdrawal pipeline. Hypernative said comparing proposed transactions with parameters normally generated by Bitget could have flagged the 18:31 test transaction before the larger withdrawals began. Hypernative said warm wallets moved $202.8 million across five networks within nine seconds at 19:16. Hypernative said limits on transfers by individual wallet tiers over short periods could have delayed or blocked much of that wave. Hypernative said secondary approval requirements could also have delayed or blocked much of the wave. Hypernative said anomalous-transfer alerts could have automatically suspended the affected signer instead of relying on manual intervention. Attacker-linked transfers continued until 21:23 UTC, almost three hours after Bitget's stated detection time. Bitget has since said it remediated the vulnerability. Bitget said no further unauthorized transfers occurred after containment. Mandiant and SlowMist remain involved in the forensic investigation. The unresolved questions are what Bitget's security systems did with the 18:31 alert and why the compromised signing route remained active long enough for roughly $290 million to leave in the two major waves.
This content is an AI-generated summary/analysis for informational purposes only and does not constitute investment advice.