September 01, 17:40
Hacker triggers 1,490 successful replays in ICON crypto exploit
How a hacker reused the same authorization message 1,490 times to trigger massive crypto payout loops
CryptoSlate
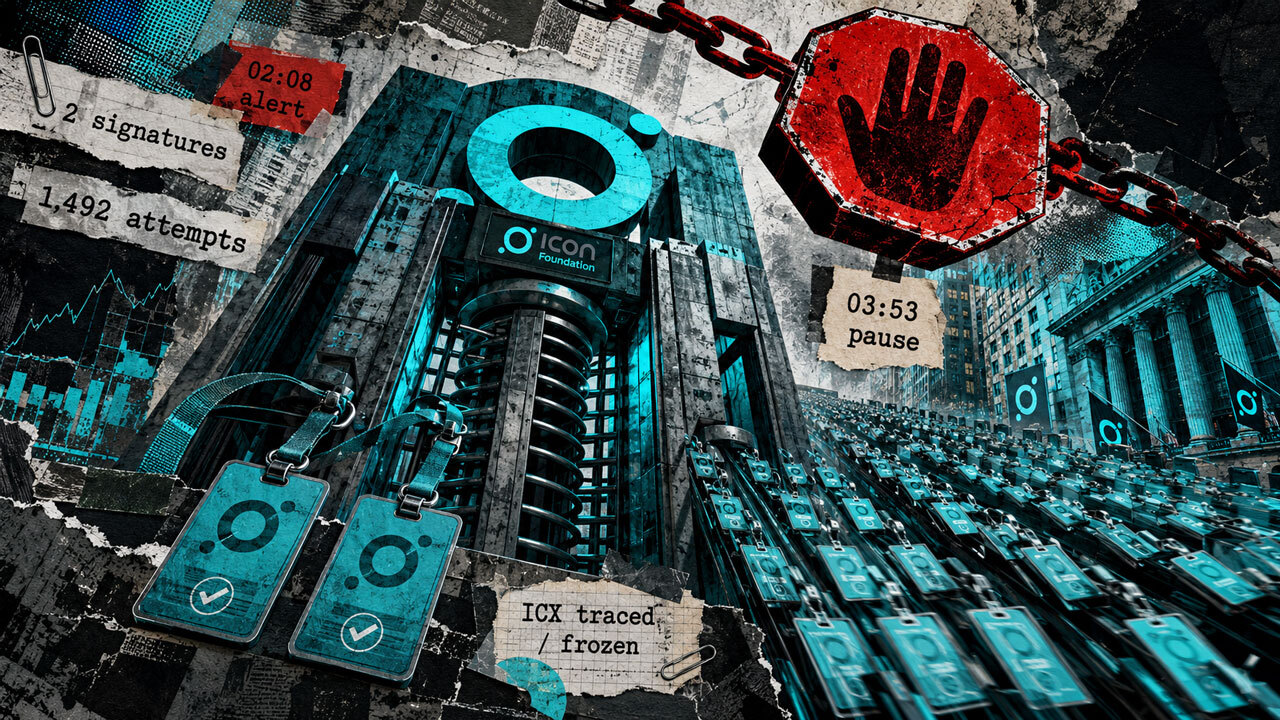
A hacker triggered 1,490 successful replays in an ICON exploit by reusing two legitimate withdrawal messages. The two messages were reused 1,492 times. The exploit released 119,866,000 ICX and 531,600 bnUSD from foundation-held assets. ICON said no user deposits, balances or positions were accessed. ICON put the net loss to date at about 150.2 ETH plus 31,204 USDC. The vast majority of the ICX was traced, frozen and under active recovery. ICON said bnUSD and SODA were recovered in full. Exchange-held amounts remain subject to revision because ICON had not received exact figures for how much ICX exchanges held, converted or withdrew. The flaw let the hacker change part of a withdrawal identifier without changing the signed payload. ICON traced the mismatch to a change that standardized withdrawal messages at 32 bytes. That change routed part of the serial number through float64-range logic instead of exact integer arithmetic. The contract's uniqueness check examined high bits that the hacker could vary. Cryptographic verification covered the unchanged low 256 bits. The signed payload and signature remained identical within each replay set. The altered unsigned portion made the calls appear unique. Two calls reverted. Every successful call credited the same relayer wallet. ICON said the flaw was specific to its implementation. Other supported chains used fixed-width integers that could not produce the same mismatch. ICON's monitoring system alerted at 02:08 UTC, seven minutes after the exploit began. Technical staff began investigating at about 03:40. The affected contract was paused at 03:53, 105 minutes after the alert. The hacker began splitting ICX across exchange deposit addresses at 02:44. The distribution continued until about 05:20. ICON said its pause could not stop funds already swept into exchange custody. The network was halted at 06:18:54. It resumed at about 07:51 the next day, roughly 25 hours later. Bitvavo, Bitget and KuCoin publicly confirmed suspensions of ICX deposits and withdrawals around the incident. None identified itself as holding the hacker's funds or verified the amount frozen. A November 2025 relay audit reviewed selected relay and verifier code, including ICON verifier files. Its published scope did not list the affected migration-contract source. None of its nine disclosed findings flagged the serial-number mismatch. ICON said incident-related relay logic had been audited. However, ICON said the gap fell outside the findings.
This content is an AI-generated summary/analysis for informational purposes only and does not constitute investment advice.