September 02, 21:10
Analysis: USDC may remain exposed until wallets and host chains migrate
USDC may be only as quantum-safe as its slowest wallet, bridge or blockchain

CryptoSlate
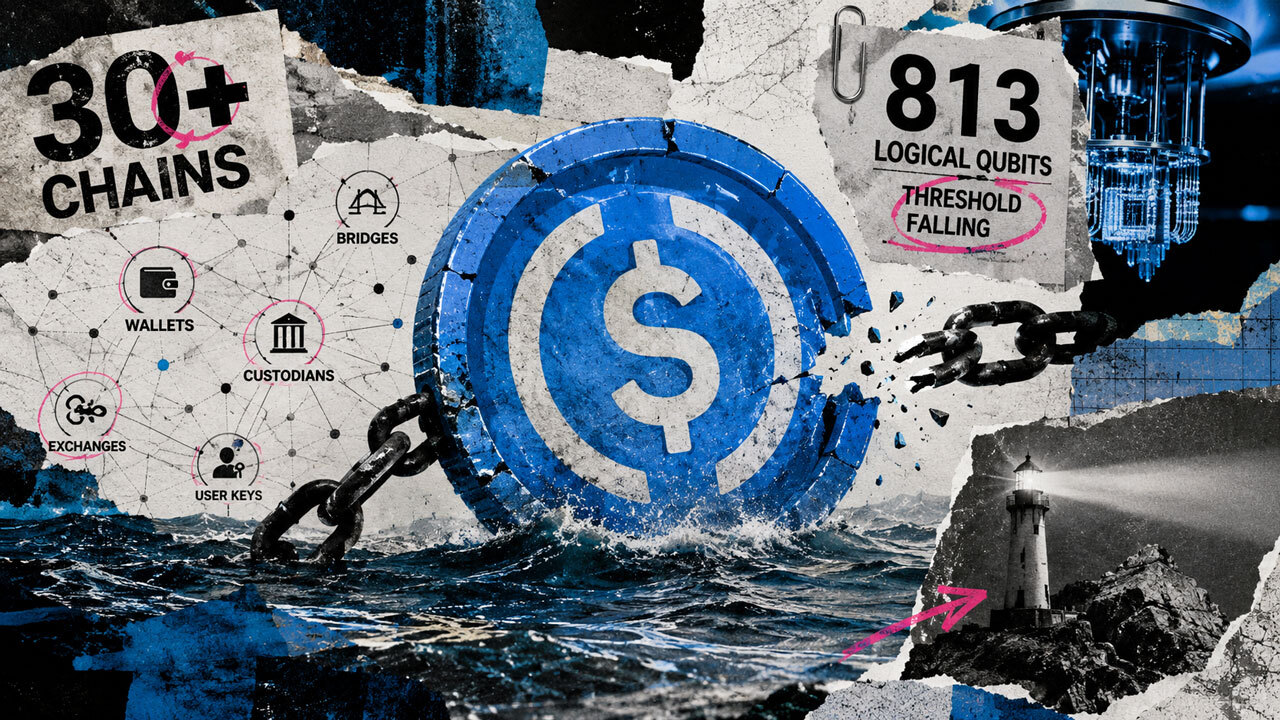
The author argues that USDC may remain exposed until wallets, custodians, bridges, users and host chains can migrate to safer transaction authorization. Circle's current contract documentation contains 37 mainnet USDC rows. Circle warned developers on Aug. 31 to inventory their cryptography, identify vendor dependencies and prepare key rotation. Circle described 813 logical qubits as the August 2026 low-width record on ECDSA.fail. The figure does not by itself describe a complete Shor attack, its circuit depth, its error-correction overhead or its runtime on physical hardware. A March 2026 paper estimated that a 256-bit elliptic-curve discrete-log attack could use fewer than 1,200 logical qubits and fewer than 90 million Toffoli gates. The paper also estimated a separate configuration using fewer than 1,450 logical qubits and fewer than 70 million Toffoli gates. That minutes-scale scenario assumed a fast-clock superconducting architecture, physical error rates of 10^-3, planar connectivity and fewer than 500,000 physical qubits. Those estimates do not provide a delivery date for such a machine. Circle's comparison with Google's Willow processor also distinguishes 105 physical qubits from 105 attack-ready logical qubits. NIST standardized SLH-DSA in FIPS 205 and says organizations should begin replacing quantum-vulnerable cryptography now. NIST's 2035 horizon concerns deprecation and removal from standards rather than a prediction of Q-day. Arc can verify SLH-DSA-SHA2-128s signatures through an execution-layer precompile. Arc's custody guide still specifies secp256k1 ECDSA transaction signing. Arc's roadmap places opt-in beta post-quantum wallet signatures at mainnet launch and post-quantum validator signatures later. Circle says Arc has not chosen its final post-quantum transaction-signature scheme and expects hybrid ECDSA support during migration. Circle's USDC page says 35 networks as of June 29, 2026 while enumerating 37 names. A separate Circle Mint table reaches 38 only when Arc testnet is included. Solana uses Ed25519 signatures. Polkadot supports sr25519, Ed25519 and ECDSA accounts. XRPL amendments need more than 80% trusted-validator support for two weeks. Algorand protocol changes require an on-chain supermajority. Stellar upgrades depend on validator consensus. Circle's token-layer controls include minting, burning, pausing, blacklisting and contract upgrades. Those controls can help contain an identified incident on a supported contract. They cannot rotate a user's private key or change a host chain's signature verifier. Users and custodians must move funds from exposed accounts through wallets and host chains that accept the destination signature. Bridge operators must protect their signing and contract controls while coordinating liquidity across both sides. Base-layer communities must approve and deploy protocol changes. Wallet makers, hardware vendors and exchanges must support old and new signatures during the transition. A workable rollout would require inventories of exposed and unexposed keys, tested destination account types, support for new signatures and recovery policies for balances that do not move. Circle can coordinate milestones for its contracts and services, but each host ecosystem would decide how and when its classical path closes.
This content is an AI-generated summary/analysis for informational purposes only and does not constitute investment advice.